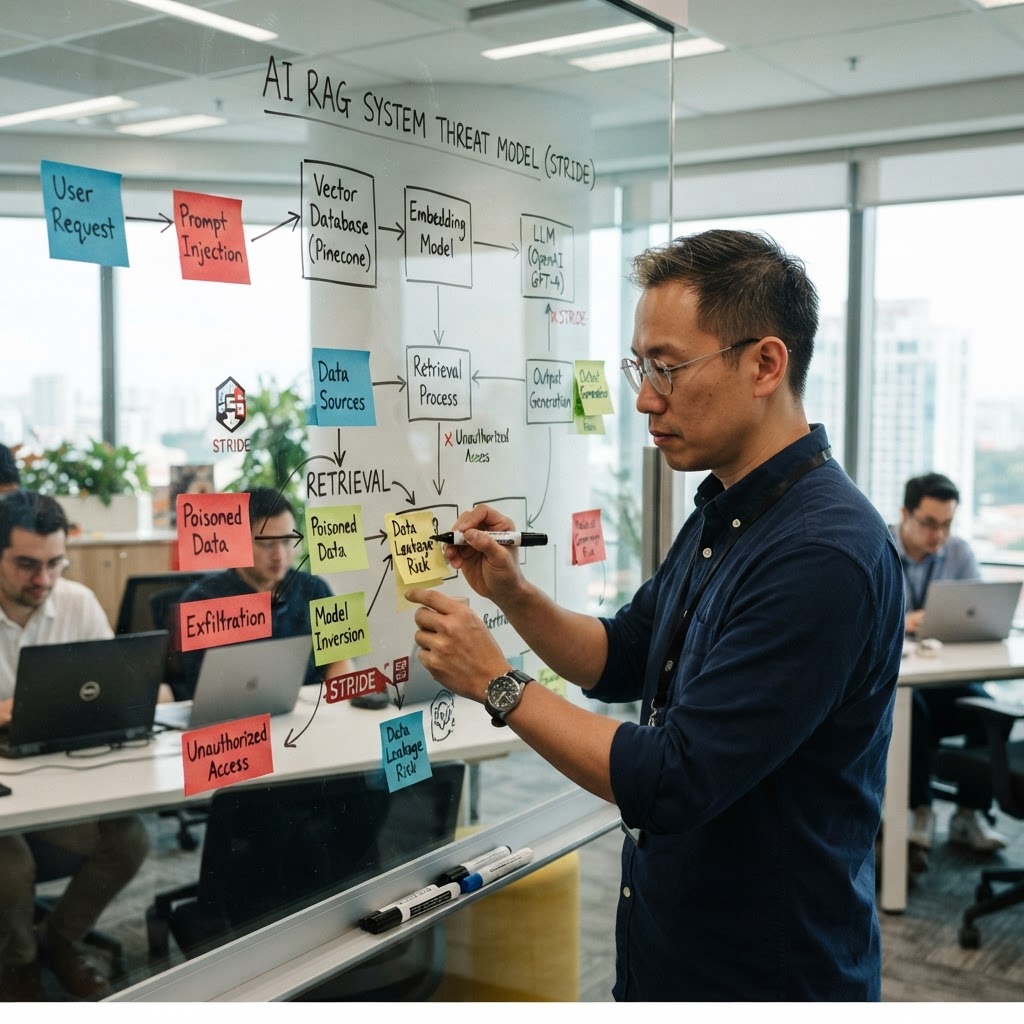
Week 1
Threat-Model an Enterprise RAG System
Client Background
CaseBrief is a legal-tech firm building a Retrieval-Augmented Generation assistant that lets lawyers query their confidential case files in natural language. The assistant embeds client case documents, stores them in a vector database, retrieves relevant chunks at query time, and forwards them to a hosted LLM to answer. Leadership approved a threat model before onboarding the first paying firm.
Business Environment
You are the AI security architect. CaseBrief shared the system architecture, data flow, and access-control design. You will produce a structured threat model (STRIDE + MITRE ATLAS) identifying the most material threats and recommending mitigations.
Security Incident
No breach; the engagement is a proactive threat model commissioned by CaseBrief leadership before onboarding the first paying law firm, driven by the firm's ethics committee requiring a documented security assessment as a precondition for handling privileged case data.
Scope
Architecture and access-control design review for the CaseBrief RAG system, covering the embedding pipeline, vector store, retrieval/re-ranker, and generation layer. Excludes source code and a deployed penetration test.
Objectives
- Enumerate components and trust boundaries of the RAG system
- Apply STRIDE and MITRE ATLAS to identify material AI-specific threats
- Identify document-tenant isolation and authorization failure paths
- Produce a threat model with prioritized mitigations
- Identify 'Legacy RAG' weaknesses in post-filter multi-tenancy and recommend pre-filter retrieval and automated PII sanitization at ingestion per ISO/IEC 42001 and the 2026 OWASP/MITRE ATLAS iterations.
Required Deliverables